-
October 7, 2026
- Share:
-

-

-

-

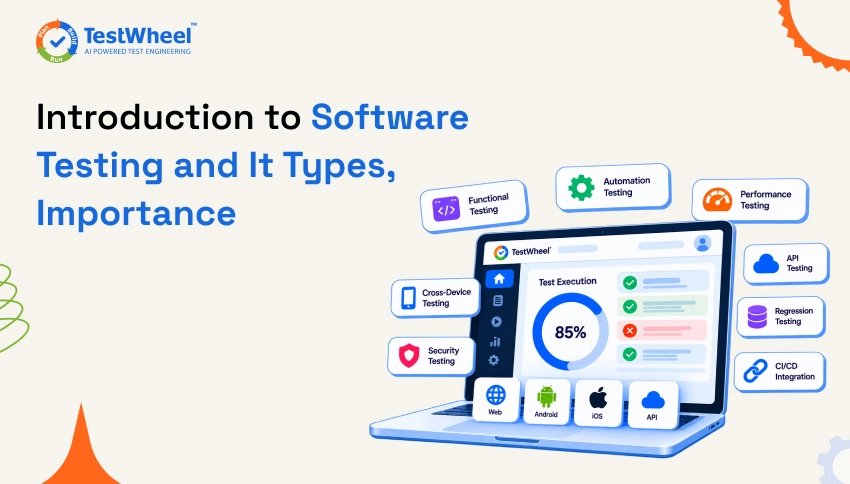
Software testing is the process of checking software before it reaches users to confirm it works the way it’s supposed to and catch problems while they’re still cheap to fix. It means running the application, comparing what happens against what should happen, and finding anything that doesn’t match quality standards.
This guide breaks down what software testing is, why it’s important, and how teams do it in 2026. If you’ve ever used an app that crashed at the worst possible moment, you already understand what software testing solves for.
For a deeper look at how testing fits into the software development lifecycle, TestWheel’s guide to QA and the software testing life cycle is a good companion read.
What is Software Testing?
Quick answer: Software testing is the process of checking any software (website, app, web app) to gauge whether it works the way it’s supposed to, before real users can access it. Testers look for bugs, confirm the software meets its technical and business requirements, and ensure it performs well under real-world conditions. Explore our software testing basic guide.
In technical terms, software testing is the process of executing a program or application with the intent of finding errors, verifying that it meets business and technical requirements, and confirming it behaves correctly under both normal and unexpected conditions.
Basically, a tester (or an automated script) drives the software through every screen, button, and workflow to see what breaks and what doesn’t
Some people use “software testing” and “quality assurance” interchangeably, but they’re not. Testing is one part of QA. QA is the broader effort to build quality into the process through code reviews, requirement checks, and process standards. Testing is the hands-on work of running software and checking the results.
Why is Software Testing Important?
Software testing is pivotal because software runs the parts of daily human life that can’t afford to fail. Banking apps move people’s savings. Hospital scheduling systems decide who gets treated and when. E-commerce checkouts decide whether a small business makes payroll.
Software failures have real-world consequences. In 2015, Starbucks had to close around 60% of its U.S. stores for several hours after a point-of-sale software update went wrong. In 2016, Nissan recalled more than 3 million vehicles worldwide over a software defect in airbag sensor detectors.
There’s also the cost factor. A bug caught while a developer is still writing the code might take minutes to fix. The same bug, found after the product has shipped, needs an emergency patch, a public apology, and hours of incident response. Choosing the right software testing tools can help teams automate repetitive checks and identify defects earlier in the development process.
This is the “cost of defects” curve, and it’s the strongest reason for software testing strategies to build in checks as early as possible.
Beyond avoiding disasters, software testing does the following:
- It builds user trust. An app that consistently works is one people keep using. One that crashes during checkout loses customers to competitors.
- It reduces the cost of fixing problems. Catching a defect during development is far cheaper than fixing it after release, when it might involve refunds, support tickets, or a damaged reputation.
- It protects revenue and uptime. For any business running on software, be it a food delivery app or internal payroll tools, downtime costs real revenue.
- It keeps teams clear on what “done” means. A feature isn’t complete because the code compiles. It’s complete when it’s been tested against real requirements and usage.
What can be Automated within Software Testing?
Automated software testing uses scripts or AI-driven tools to run test cases, compare the actual result to the expected one, and flag anything that doesn’t match. All this is done without someone manually repeating the same clicks every time.If you’re new to automation, an automated testing tutorial for beginners can help you understand the basics and get started with your first automated tests.
Imagine checking a login form after every single code change a team makes. If a team pushes ten updates a day, checking that login form by hand ten times a day gets old fast, and testers start skipping steps because they’re tired or short on time.
An automated test does the same check in seconds, every time, without getting bored or careless.
Here’s what typically gets automated first, because it delivers the most value for the least effort:
- Regression testing: Re-running old test cases to confirm that new code hasn’t broken something that used to work. This is the most common use of automation.
- Smoke and sanity checks: Fast, shallow tests that confirm the build didn’t break in an obvious way before deeper testing begins.
- Cross-browser and cross-device checks. Running the same test across Chrome, Safari, Firefox, and different screen sizes without manually repeating the process on each one.
- Load and performance testing. Simulating hundreds or thousands of users hitting an application at once.
- API testing. Sending requests to backend services and validating the responses. Naturally suited to scripts since there’s no visual UI involved.
What usually stays manual is exploratory testing (where a tester uses the software naturally, looking for problems nobody thought to write a test case for), usability testing (judging whether something feels intuitive), and early-stage testing on features that are still changing day to day.
TestWheel’s breakdown of what makes automated tests successful covers this split in more depth.
Levels of Software Testing
Software testing operates at different levels. Each one checks a different scope of the system, from a single function up to the entire product working together.
First, you test each part individually. Then you test how parts work together. Then you test the whole assembled ecosystem. Finally, the customer test-drives it to confirm it meets their expectations.
1. Unit testing
Developers test individual functions or components in isolation before code is merged into the main project. If a function is supposed to calculate a discount, unit testing checks that it returns the right number for a range of inputs, including edge cases like a $0 order or a 100% discount code.
2. Integration testing
Once individual units pass, integration testing checks how they work together. A shopping cart function might work fine alone, and a payment function might work fine on its own, but integration testing confirms that the cart hands off the correct total to the payment system.
3. System testing
This level tests the complete, integrated application as a whole, checking it against the full set of requirements. It’s where testers verify that the entire user journey (browsing a product, adding it to a cart, checking out, and receiving a confirmation) works end to end.
4. Acceptance testing
The final level, often called User Acceptance Testing (UAT), is where real users or stakeholders confirm the software solves their problem and is ready to ship. Even a technically flawless application can fail here if it doesn’t give users what they need.
Types of Software Testing and their Differences
Software testing types are usually grouped into two buckets: functional testing (does it do what it’s supposed to do?) and non-functional testing (does it do it well?).
But first, here’s a list of software testing types you’ll run into most often:
- Regression testing. Re-checks existing features after a code change to make sure nothing that used to work has broken.
- Smoke testing. A quick, shallow check right after a new build to confirm the basics work before anyone invests in deeper testing.
- Sanity testing. A narrow, focused check on a specific fix or feature, done after smoke testing passes, to confirm that particular change works as intended.
- Exploratory testing. Unscripted testing where a tester actively explores the application, trying to break it in ways a written test case does not anticipate.
- Usability testing. Checks whether real users find the software easy and intuitive to use day-to-day.
- Security testing. Looks for weaknesses an attacker could exploit, like poor password handling, exposed data, or unprotected API endpoints.
- Performance testing. Measures how the software behaves under load, including speed, stability, and how many users it can handle at once.
- Compatibility testing. Confirms the software works correctly across different browsers, devices, operating systems, and screen sizes.
- Accessibility testing. Checks whether people using screen readers or other assistive technology can use the software effectively.
Most real projects use multiple types. A healthcare scheduling app might lean on security and functional testing because patient data and appointment accuracy are a key priority. A high-traffic news site might prioritize performance testing so the homepage doesn’t glitch during a breaking story. The right combination depends on what’s at risk if the software fails.
What is SDLC testing?
The Software Development Life Cycle, or SDLC, is the overall process a team follows to build software, from the first idea to the final release and beyond. It includes these phases: requirement gathering, design, development, testing, deployment, and maintenance.
“SDLC testing” refers to how testing fits inside that bigger picture. In older waterfall model projects, testing was its own separate phase that happened after all the coding was done. It was a final inspection at the end of a factory line.
The problem with that? Bugs found this late are the most expensive and time-consuming to fix, since the team has already moved on to other work.
Modern teams build testing into every SDLC phase, an approach called “shift-left”. Testing moves earlier, i.e left on the project timeline. Requirements get reviewed for testability before code is written. Developers write unit tests alongside their code. QA teams start designing test cases during the design phase instead of waiting for a finished build. The goal is to catch a problem when it’s still easy to fix.
What is STLC testing?
The Software Testing Life Cycle, or STLC, is the set of phases a QA team follows within the broader SDLC, focused on the testing effort itself. Where SDLC covers the whole product’s journey, STLC keys in on how testing gets planned and executed.
The STLC usually includes:
- Requirement analysis. Testers study the requirements to understand what needs to be tested. They flag anything unclear or untestable.
- Test planning. The team decides on scope, timelines, tools, and resources needed for the testing effort.
- Test case design. Testers write out the specific steps, inputs, and expected outcomes for each test.
- Environment setup. A test environment is configured to replicate the production environment as closely as possible, so results are reliable.
- Test execution. Testers (or automated scripts) run the test cases and log the results.
- Test closure. The team reviews what was tested, what defects were found and fixed, and documents lessons for the next cycle.
Following a structured STLC keeps testing accountable. It answers questions like who tested what, how much of the application was covered, and how many defects were caught before release.
Functional vs. Non-Functional Testing
This is one of the most common points of confusion for people new to software testing.
Functional testing checks what the software does. For example, does clicking “Add to Cart” actually add the item to the cart? Does entering the correct password log you in?
Functionality testing software lets testers compare what a system does against what it’s supposed to do, based on the written requirements.
Non-functional testing checks how well the software does what it is supposed to. For example, it doesn’t care whether the login works in principle. It cares whether the login is fast, secure, usable on a small phone screen, and stable when 10,000 people try to log in at the same time.
| Features | Functional testing | Non-functional testing |
|---|---|---|
| Checks | Features and business logic | Performance, security, usability, reliability |
| Answers the question | Does it work? | Does it work well? |
| Example | Does the “forgot password” link send a reset email? | Does the reset email arrive within 5 seconds under normal load? |
| Common types | Unit, integration, system, regression | Performance, security, usability, compatibility |
| Who typically cares most | Product managers, business analysts | Site reliability engineers, security teams, end users |
A banking app with flawless functional testing but poor security testing is a data breach waiting to happen. A fast app that doesn’t process payments correctly is useless. A solid QA process treats both forms of testing as equally important. Explore more about the functional and non functional testing.
Manual vs Automated Testing
Manual testing means that a person sits down and works through the application by hand. They click buttons, fill in forms, and compare what happens against what should happen. Automated testing means a test script or AI-driven tool does the same work, running the same steps faster and more consistently than a human.
Neither approach replaces the other.
Manual testing is still better for exploratory testing, usability judgments, and features that are still changing shape, since automating something that will be redesigned next week wastes effort.
Automated testing is the better choice for anything repetitive: regression suites, cross-browser checks, and tests that need to run every time code changes.
Rule of thumb: if a test needs human judgment about whether something “feels right,” keep it manual. If a test just needs to confirm the same known result every time, automate it.
QA teams run a mix of both, with automation handling the repetitive volume and manual testers focused on the areas that need a human eye. TestWheel’s manual vs automated testing comparison goes further into how teams decide.
Best Practices for Software Testing
Good software testing boils down to running the right tests, consistently, and acting on what you find. These best practices will help catch problems early:
- Write test cases from the requirements, not from the code. Testing what the code does, instead of what it’s supposed to do, confirms the bug is consistent. It doesn’t catch the bug.
- Test early and often. If you wait until the end of a sprint or release cycle to start testing, defects pile up and get more expensive to fix.
- Keep test data realistic. Testing with a database of five clean records won’t catch what happens when a real customer enters a 40-character name or a non-existent discount code.
- Track defects properly. A bug that’s found but not logged, prioritized, and followed up is essentially invisible.
- Review and retire old test cases. A test suite that isn’t pruned eventually slows everyone down and starts testing features that don’t exist anymore.
- Make test results visible to the whole team. Developers, product managers, and QA all need to see the same reporting, not three different spreadsheets.
How is Software Testing conducted?
In practice, most teams follow a version of this cycle for every feature or release:
- Requirement review. Testers read through the requirements and ask questions before writing any test case. A lot of ambiguity gets caught here.
- Test planning. The team decides what needs testing, how deep to go, and which types of testing (functional, performance, security, and so on) apply to each release.
- Test case creation. Specific, step-by-step test cases are written, including the exact inputs and expected results.
- Test environment setup. A dedicated environment, separate from production, is prepared so tests don’t accidentally affect real users or real data.
- Execution. Testers or automated scripts run the test cases and record what actually happened.
- Defect logging and retesting. Anything that doesn’t match the expected result gets logged as a defect, is sent to developers, and is retested once it’s fixed.
- Reporting and sign-off. Results are summarized for stakeholders, and the release either gets a green light or goes back for more work.
This cycle repeats for every major code change, which is why manual repetition quickly becomes a bottleneck; automation is a non-negotiable at that point.
Best Practices for Software Testing (reduce risk and cost)
These few practices go a long way in finding bugs when they are still cheap and easy to fix:
- Shift testing left. The earlier a defect is found, the cheaper it is to fix. A bug caught during code review might take ten minutes. The same bug caught by a customer in production will need emergency fixes and reputational damage that costs a lot more.
- Use risk-based testing. A typo in a footer link is a minor annoyance. A bug in the payment flow is a business emergency. Risk-based testing means spending more effort on the parts of the application where failure would hurt the most.
- Automate the repetitive, high-volume checks. Every hour spent manually re-running the same regression suite is an hour not spent on exploratory testing or judgment calls that need a human. Automating that repetitive work directly reduces cost per release.
- Build a real test environment. If the test environment lacks the same data volume, integrations, or configurations as production, results won’t be reliable.
- Catch flaky tests before they impact trust. A test that sometimes passes and sometimes fails for no real reason trains a team to ignore failures. Flaky tests need to be fixed or removed.
Testing Methodologies and Techniques
A methodology is the high-level approach a team takes to organize and plan testing. A technique is a specific method used to design individual test cases. Here are the ones that come up most often.
Testing Methodologies
- Waterfall testing. Testing happens as a distinct phase after development is complete. It’s easy to plan, but all bugs are caught when they are hardest to fix, towards the end.
- Agile testing. Testing happens continuously, alongside development, in short cycles (sprints). This is how most modern software teams work.
- The V-model. Each development phase has a corresponding testing phase planned at the same time. Requirements pair with acceptance testing, design pairs with system testing, and so on.
Testing Techniques
- Black-box testing. Testers check the software’s inputs and outputs without looking at the underlying code, the same way a customer would. Most functional tests rely on this technique.
- White-box testing. Testers examine the internal code structure, checking logic paths and coverage. This is mostly used at the unit testing level by developers who wrote the code.
- Gray-box testing. A mix of both: the tester has some knowledge of the internal workings but tests primarily from a user’s perspective. Common in integration and security testing.
- Exploratory testing. Instead of following a pre-written script, testers actively investigate the application, using what they learn to decide what to test next. It catches bugs nobody thought to write a formal test case for.
A well-rounded software testing strategy usually blends several of these. A team might use Agile testing as its overall rhythm, black-box testing for most functional checks, and exploratory sessions before a major release.
The Future of Software Testing
Software testing is changing faster than it has in years because of two pressures: release cycles keep getting shorter, and applications keep getting more complex. They are causing the following shifts:
- AI-driven test creation and maintenance. Instead of writing every test step in code, AI tools can now generate test cases from plain-English instructions and even fix themselves when the application’s UI changes. This is often called self-healing. It saves hours otherwise spent fixing tests that broke not because of a real bug, but because a button moved or a label changed.
- No-code and low-code testing. Automation used to require someone who could write Selenium or Java scripts. No-code platforms let testers without a programming background build full automated suites using recorded actions or plain-language instructions.
- Continuous testing inside CI/CD. As teams ship code multiple times a day, testing has to run automatically on every commit. Continuous testing embeds automated checks directly into the build pipeline, so a broken change gets flagged in minutes.
- Shift-right and testing in production. Alongside shift-left, more teams now also embrace “shift-right,” i.e., monitoring real user behavior and system performance after release to catch issues that only show up at real-world scale.
Why choose TestWheel for Automated Software Testing?
TestWheel is a cloud-based, AI-driven test automation platform that enables the full testing lifecycle (web, mobile, API, performance, and desktop testing) from a single account. It’s a practical fit for teams working through everything covered in this guide.
TestWheel is best for teams that want AI-powered, no-code testing without hiring a team of automation engineers. Testers write steps in plain English, like “open the login page, enter the username, tap sign in,” instead of writing scripts. That means people without a coding background can build and run real automated test suites.
When the application’s UI changes (a button moves, a label gets renamed), TestWheel’s self-healing engine updates the affected tests automatically. Existing Selenium scripts can be uploaded and converted into TestWheel’s no-code format, so teams don’t have to throw away work they’ve done.
TestWheel already supports work for the U.S. Air Force on the Defense Property Accountability System (DPAS). In a verified customer review on AWS Marketplace, the team running that program said TestWheel saves them over 10 hours out of every 40-hour user acceptance testing cycle.
If your team is still deciding how much to automate and where to start, TestWheel’s free plan is a reasonable way to test the approach on a real project before committing further.
Final Takeaway
Software testing isn’t a single task you can check off a list. It’s an ongoing discipline that touches every level of the software, from a single function to the finished product a customer uses.
The teams that handle it well test the right things, at the right level, as early as they reasonably can. They build a process that catches problems while they’re still cheap to fix.
Whether you’re just starting to learn software testing or you’re deciding how to structure a QA process for a growing team, the fundamentals in this guide will give you the foundation.
If you want to see how a modern, AI-driven platform handles that foundation in practice, you can explore TestWheel or start a free trial to run your own tests firsthand.
FAQs for Software Testing
Software testing is the process of checking software before it reaches users to find bugs and confirm it does what it’s supposed to do. It’s the same idea as proofreading an essay before you submit it, applied to code instead of writing.
The two broad categories are functional testing (checking that features work correctly) and non-functional testing (checking performance, security, and usability). Within those, common types include regression, smoke, sanity, exploratory, usability, security, performance, and compatibility testing.
SDLC (Software Development Life Cycle) covers the entire process of building software, from requirements to deployment and maintenance. STLC (Software Testing Life Cycle) is the specific set of phases within that process focused only on testing, such as test planning, test case design, and execution.
Not exactly. Testing is the hands-on work of running software and checking results. QA (quality assurance) is the broader effort to build quality into the entire process. It includes reviews and standards, with testing as one part of the picture.
No, not entirely. Repetitive tasks like regression testing, cross-browser checks, and API testing are strong candidates for automation. Exploratory testing and usability judgments still benefit from a human tester, since they rely on subjective judgment that automation can’t fully replicate yet.
Manual testing is done by a person clicking through the application by hand. Automated testing uses scripts or AI-driven tools to run the same checks faster and more consistently. Most teams use a mix of both.
It catches defects before they reach users, which protects revenue, reduces the cost of fixing problems, and builds customer trust. Skipping it will delay discovery of those defects until they’re more expensive to fix.
Strong analytical thinking, attention to detail, clear communication, and curiosity matter more at the start than any programming language. Get familiar with common testing types and at least one testing tool when you’re ready to specialize.
Regression testing re-runs existing test cases after a code change to confirm no existing functions have broken. It matters because new code can unintentionally disrupt what was working before.
AI is increasingly used to generate test cases from plain-English instructions. It can also automatically fix, or “self-heal,” tests when an application’s UI changes. This reduces the maintenance work that used to make test automation expensive to keep up with.